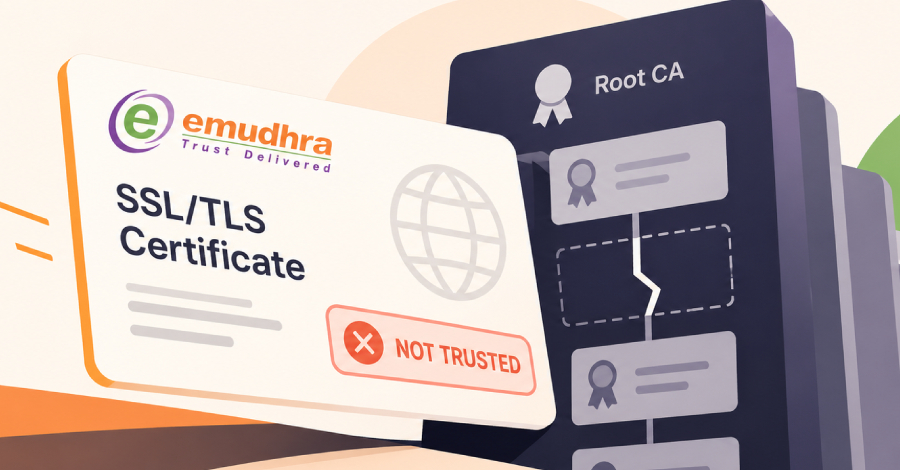
eMudhra to Exit Global SSL/TLS Business After 8 Intermediate CA Keys Found Easily Guessable
Read More eMudhra, an Indian certificate authority (CA), will withdraw from its global SSL/TLS certificate business, its board decided on Thursday. The decision came five days after a researcher reported recovering the private keys of eight of its intermediate CA...
ThreatsDay: AI Secrets Leak, PingCAP Source Theft, Signal Hang-Up Flaw, Laravel Auth Bypass + 21 More
Read More This week has already been rough for cybersecurity. Critical PHP and GitLab RCE flaws, serious Linux security bugs, compromised eMudhra certificates, a Node.js RCE flaw, a hacked LiteLLM release, and hundreds of hijacked Tor relays. That’s a lot to...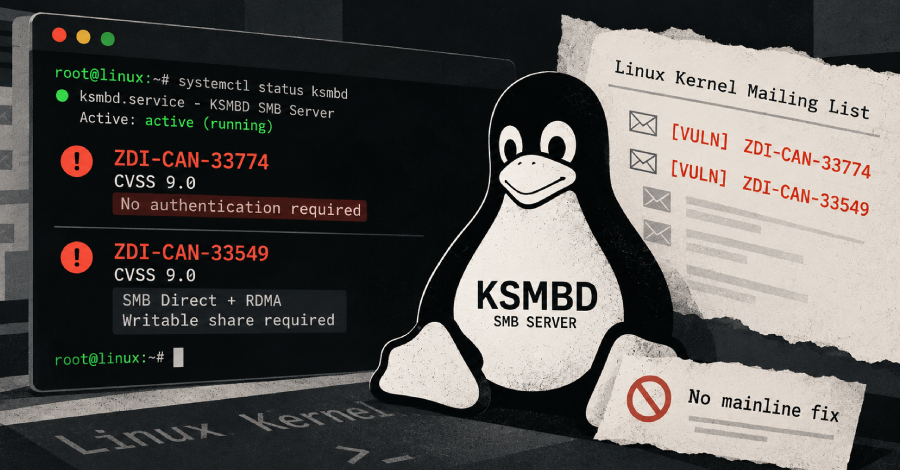
Two CVSS 9.0 Linux KSMBD RCE Flaws Disclosed on Public Mailing Lists Before Kernel Fixes
Read More Linux servers running KSMBD, the kernel’s built-in SMB server, are exposed to two publicly reported remote code execution flaws rated 9.0 by Trend Micro’s Zero Day Initiative, with no fix yet in the mainline kernel. One of them, ZDI-CAN-33774,...